SigmaStudio Using Wrong Safeload Address
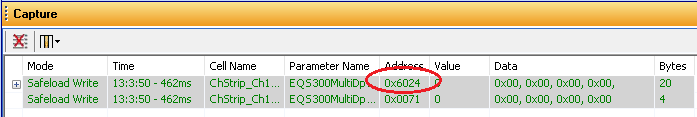
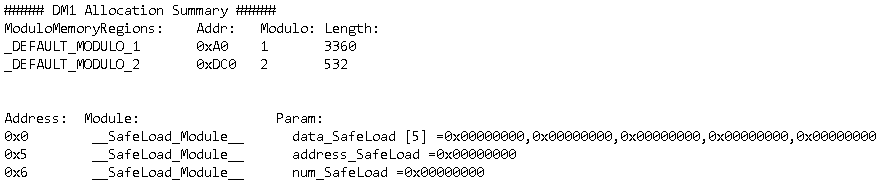
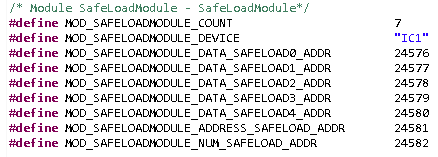
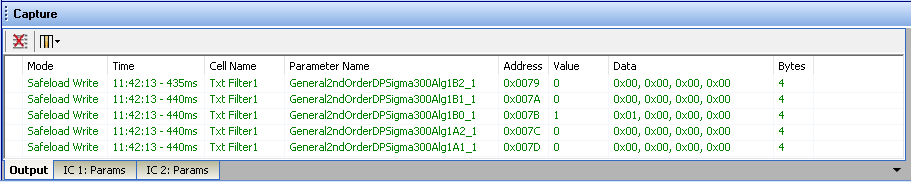
I'm working with ADAU1450 and SigmaStudio v3.15.3 Rev1741 connected via USBi interface on SPI. I noticed that whenever I change an EQ block, SigmaStudio uses "Safeload Write" operation to push the command to the DSP. The thing is, it uses 0x6024 as the safeload address while the compiler output says 0x6000 should be the correct one.
Capture window:
Compiler log:
*_PARAM.h:
Am I doing something wrong or is this a bug? And is there a workaround for this?
Audio Signal Processors
adau1450
SigmaDSP Audio Processors
Hello ,
I assume things are all working correctly?
The address you see is the address of the target object of the safeload write. SigmaStudio does hide some of the details of what is going on. If you would monitor the traffic to the DSP you would see that it is writing to the safeload write area the contents that you see (the data) to the address listed. But it is first stored in the safeload memory locations as data and a target address.
I suspect if you look in your system output files, the EQ object is residing at memory location 0x60024. And this would be the first filter coefficient, note there are 20 bytes written. That would be five 32 bit words starting at address 0x60024.
Dave T
.
Hi Dave,
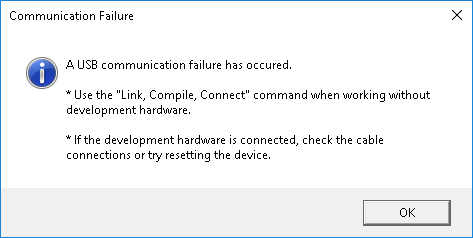
Unfortunately it's not working. I just noticed that the first time a try changing an EQ block after opening and compiling the project file, it gives me this error. When the error happens and afterward, nothing comes out of the 10p header so I couldn't get any reading at all.
The USBi is connected to the PC. It does this whether or not the 10p header is floating or connected to the hardware. It only does it when I modify an EQ block, which coincidentally uses safeload write. It also seems to be doing this with an EQ block that has "Slew" in the name.
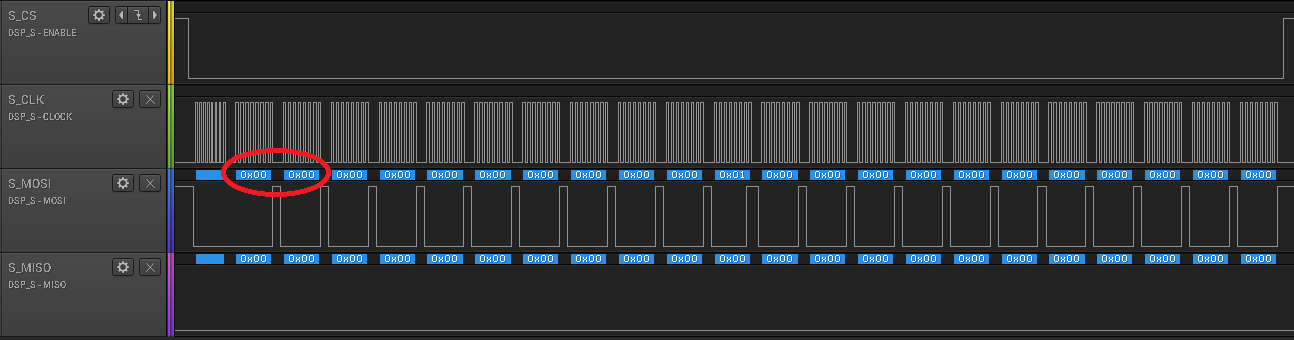
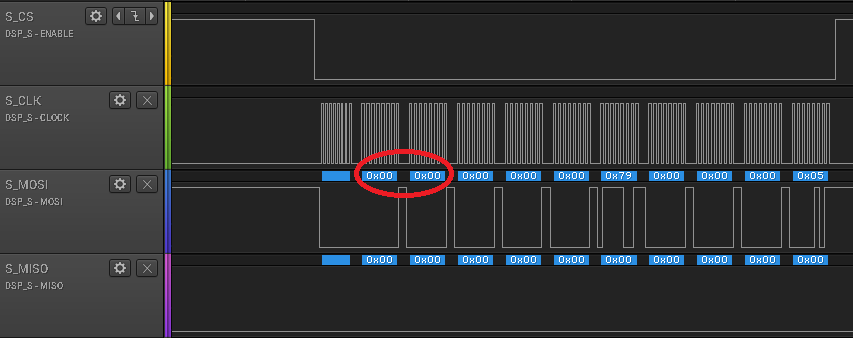
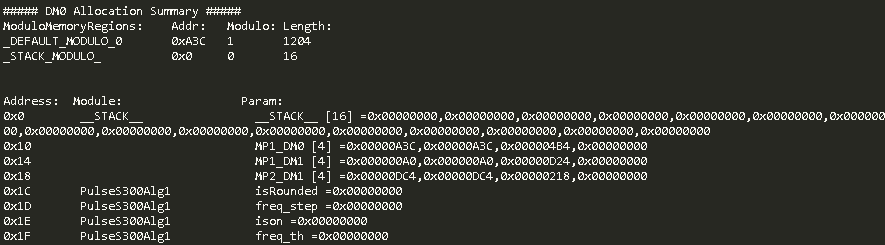
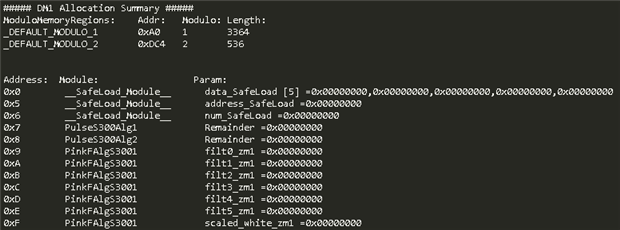
If I use any EQ block without "Slew", SigmaStudio doesn't give me the "Communication Failure" message and I can see data being pushed out of the 10p header. However, the data is still wrong. The safeload address used is 0x0000 while it's supposed to be 0x6000. So I assume it writes to the Stack instead of the Safeload memory location?
Capture output:
Pushing the 5 coefficients:
Pushing target address and number of words:
Compiler log:
-Althaf



HI Althaf:
This is very strange. I don't recall bumping into this problem in the past. Apologize for the hassle. Any chance you can send us the project that is misbehaving for us to replicate the behaviour?
thank you
Miguel
Hi Miguel,
Please find the project file attached.
-Althaf
Please log in to reply.